

Attack chain on Microsoft 365 Copilot demonstrated: from prompt...
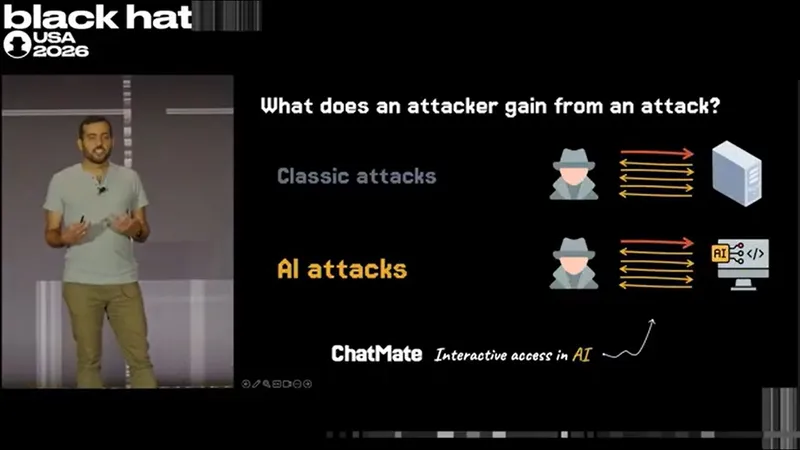
AI-generated summary A Rubrik Zero Labs researcher demonstrated an attack chain on Microsoft 365 Copilot moving from a prompt injection in a Word document to a sandbox escape via a vulnerability in Azure Kubernetes Service. Microsoft patched the vulnerability tracked as CVE-2026-32193 and paid a bounty of $48,000 for the report.